
14.07.2026
how much is the phish? the scammer claims to have paid for an article and requests payment data, the fake customer wants paypal then says paypal blocked the transaction and sends a bunch of mails that claim the article is […]
how much is the phish? the scammer claims to have paid for an article and requests payment data, the fake customer wants paypal then says paypal blocked the transaction and sends a bunch of mails that claim the article is […]

… is of course very very critical infrastructure, blunders in this area will have devastating consequences for the whole globe. this time it is luckily only the CLIENT ssh side that is affected libssh2 is a client-side C library implementing […]

btw glassdoor is indeed both sites have to be regarded as fraudulent because companies without good HUMAN BASED support hotline will be more prone to scam (possible fake scam job offers indeed.com and no way to report it) Type of business […]
USE THUNDERBIRD NOT OUTLOOK! DO NOT CLICK ANY LINKS! OR ENTER ANY DETAILS! NO MATTER HOW URGENT THINGS MIGHT LOOK! CAREFULLY INSPECT ALL LINKS IN MAILS OR WHATSAPP OR SMS! WHEN IN DOUBT PHONE THE SENDER!

another update massive amounts of cyber issues https://wordpress.org/documentation/wordpress-version/version-7-0-3/ the positive [+] always first: wordpress devs have managed to keep updates high quality (in 5 years time nothing was broken after update) this only can be acchieved with massive quality (use […]

it is a common thing and a massive traffic causing annoyance… somewhere someone tries all possible usernames for ssh: this bunch of iptables/nftables scripts will: create a list of blockable IP adresses every 3h and thus block those IPs for […]

Supply chain threat: Critical vulnerability discovered in Google’s Gemini CLI Security experts at Pillar Security have discovered a critical vulnerability in Gemini CLI, the open-source tool that brings Google’s AI assistant Gemini directly into the terminal. The flaw allowed attackers […]

once more allowing macros in documents is what made word.doc and excel.xls so dangerous and adobe pdf allowing javascript could be just that

software minimalism please! what is axio? a JavaScript library npm package for https://nodejs.org used to make asynchronous HTTP requests (WHY do devs need a PACKAGE to make http(s) requests??? any serious language can do that without a 3rd party package) […]

WARNING! ALL THIS AI EXPERIMENTATION CAN MESS UP A SYSTEM AND SHOULD ONLY BE DONE IN A VM SANDBOX! PLEASE BE CAREFUL DESPITE THE PRIVACY PROBLEM, GIVING OPENCLAW API ACCESS TO 3rd PARTY (ChatGPT by OpenAI or claude by Anthropic) […]

convenience vs security: it’s always a tradeoff credit card scammers and scimmers: when the shop owner HIMSELF is the thief if not already put all cards with “wireless” functionality (bank ec credit id healthcare cards maybe even drivers licence) into […]

cybersecurity wise mankind is doomed if mad CEOs (on drugs?) think it’s a good idea to allow the most bizare embedding of software into word.doc, excel.xls, just-want-to-print-that-file-properly.pdf and other formats “Use-after-free vulnerability in Adobe Reader and Acrobat 10.x before 10.1.9 […]

in the article how to generate a ssh key Ed25519 is the new DEFAULT STANDARD to be used to stay secure (for now) problem: loads of platforms also banks are still using RSA for https for online bankind F*** RSA […]
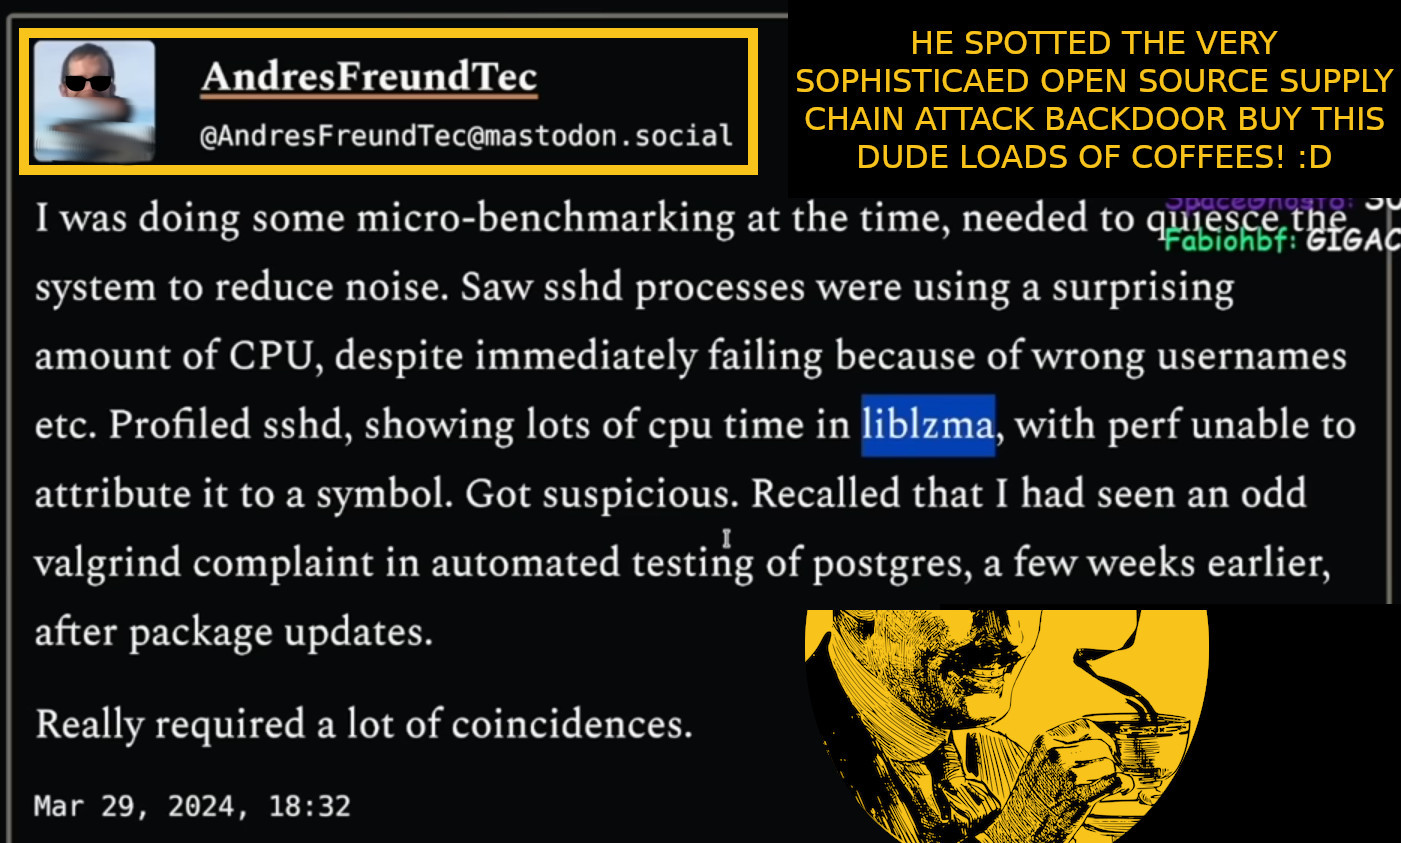
it might be the biggest “cyber” story of the year 2024 already: buy this guy MANY MANY COFFEES! he spotted the problem via know how but also luck 😀 it was a VERY VERY LONG and WILD COMPLEX and HIGHLY […]
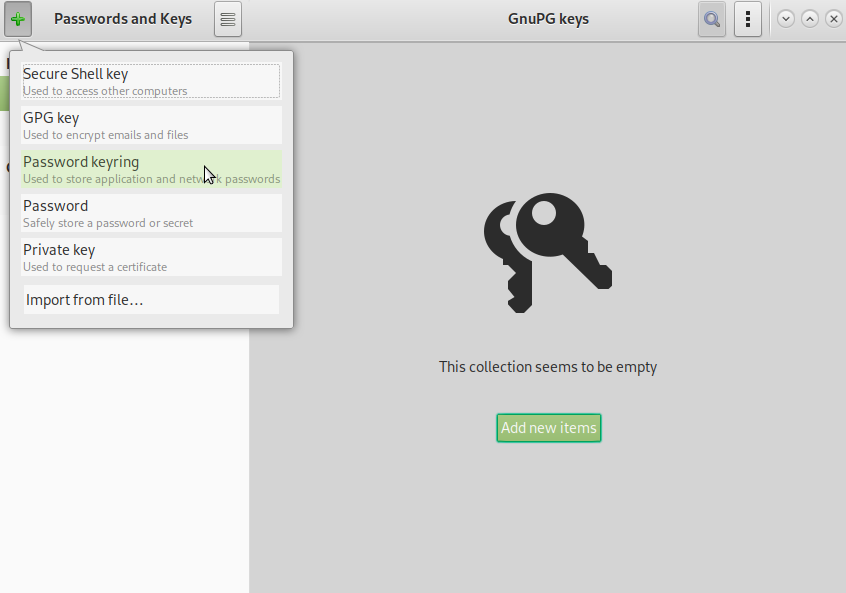
keyring is a file that stores all sorts of (for example wifi) passwords encrypted Gnome2 based MATE per default creates keyring here: ~/.local/share/keyrings/login.keyring so if the keyring password is lost, only a new keyring can be created. rm -rf ~/.local/share/keyrings/login.keyring […]
Hetzner is already doing it with very energy efficient Ampere ARM servers delivering world-class-cost-and-energy-saving-virtual-servers. (Gigabyte has them as well UNTESTED!) #SuperCharge #IT processes with #OpenSource + #GNU #Linux (call it #GNU #Linux and give the dude that wrote gcc some […]
“execute built-in macros without warning” https://nvd.nist.gov/vuln/detail/CVE-2023-6186 why copy bad concepts aka mistakes? why repeat mistakes? NO MACRO LANG JAVASCRIPT BS SHALL BE EMBEDDABLE IN ANY FORMAT, NOT IN WORD.DOC NOT IN WRITER.ODT NOT FILE.PDF! UNLESS U ACTUALLY GET PAID BY […]
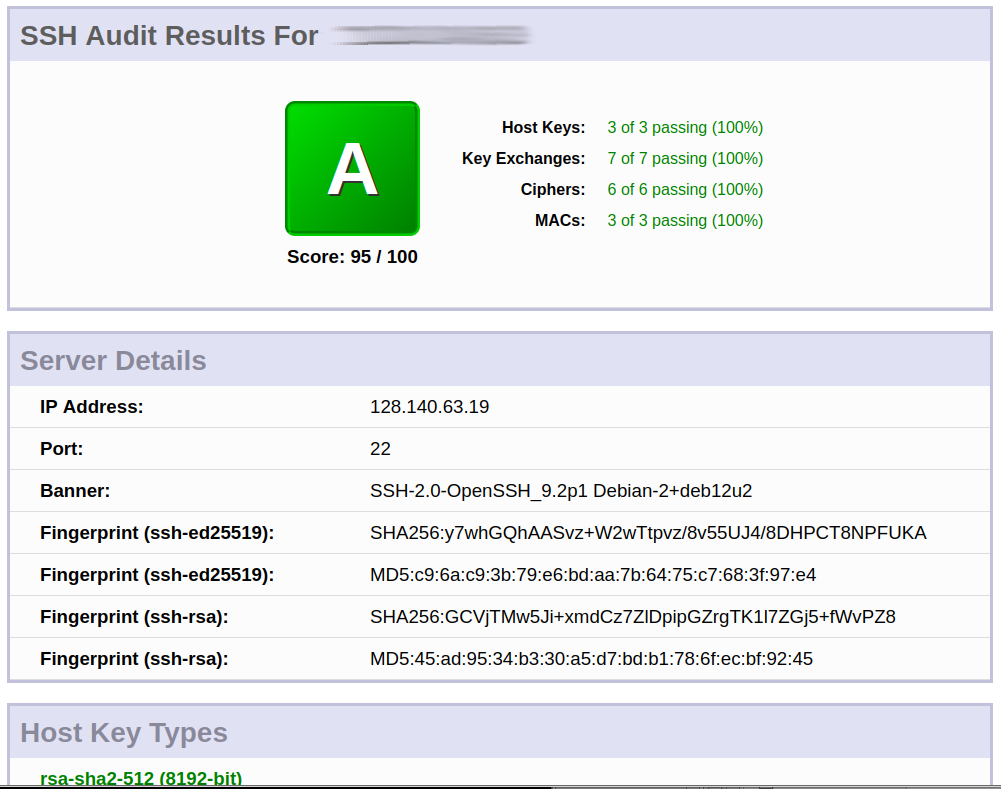
update: 2024-06: ed25519 is currently “the way to go” ssh can be regarded as “critical core infrastructure” time spend on it’s security is time well spend time + money well invested: https://www.openssh.com https://github.com/openssh current manpage: ssh.man.txt WARNING: this howto guide […]
this might be the ULTIMATE motivation to make companies (!) (finally?) migrate to GNU Linux? No? ‘The company also plans to publish further findings on the activities in Microsoft’s network in the future. Why the company does not manage to […]
GNU Linux howto ssh sshd config hardening security guide per default Debian (unfortunately) does not log ssh logins (why? afraid of harddisk overflows?) every user and admin wants to see “who and what is going on” the system usefull also […]
ssh next to https (TLS/SSL) is probably THE most essential building block of secure (unhacked) open source networked computing. CVE-2023-48795 is a (wo)man-in-the-middle-attack, so an attacker would have to sit on the same network (LAN) or somewhere between ssh client […]
vendors & users can do: keep firmware and apps as up to date as possible this requires that vendors also publish patches for critical security problems for old devices (!!! AVM Fritz does it, Samsung & Apple can too!) install […]
https://source.android.com/docs/security/bulletin/2023-12-01?hl=en <- unfortunately does not export an RSS feed so a user needs to write a converter-aggregator https://www.heise.de/news/Patchday-Android-Android-11-12-13-und-14-fuer-Schadcode-Attacken-anfaellig-9548839.html as seen in https://www.heise.de/security/rss/alert-news-atom.xml for the news junkies – how to read news in the 21st century (APPs & RSS FEEDS) – […]
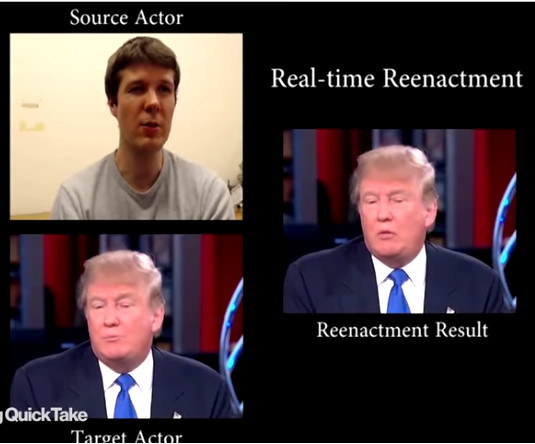
https://www.youtube.com/watch?v=UheOilps2zQ “know in some countries they believe Telegram is safe. I will show you how safe it is,” he said, before showing a screen in which he appeared to scroll through the Telegram contacts of one Kenyan strategist https://www.theguardian.com/world/2023/feb/15/revealed-disinformation-team-jorge-claim-meddling-elections-tal-hanan SS7 […]
a well faked Mail Attachment.pdf.zip was opened by a team member, infecting a (Windows 10?) PC in the background browser login tokens in the form of cookies & browser passwords were exfiltrated mail attachments are STILL the #No1 threat in […]
(knowing that manually auto-translating Russian CyberSec news to English, is not a feasable concept and need to be automated, but as this blog is non-profit, it is for curiosity.) Booking.com found an authentication vulnerability that allows account hijacking A vulnerability […]
JavaScript screwed up …. AGAIN! (another example for “why is it NOT cool for executable script languages to be allowed to embedd into PDF or any other file format”) used to steal BILLIONS of NF… ucking Ts: https://research.checkpoint.com/2022/how-hackers-make-nfts-disappear/ really should […]
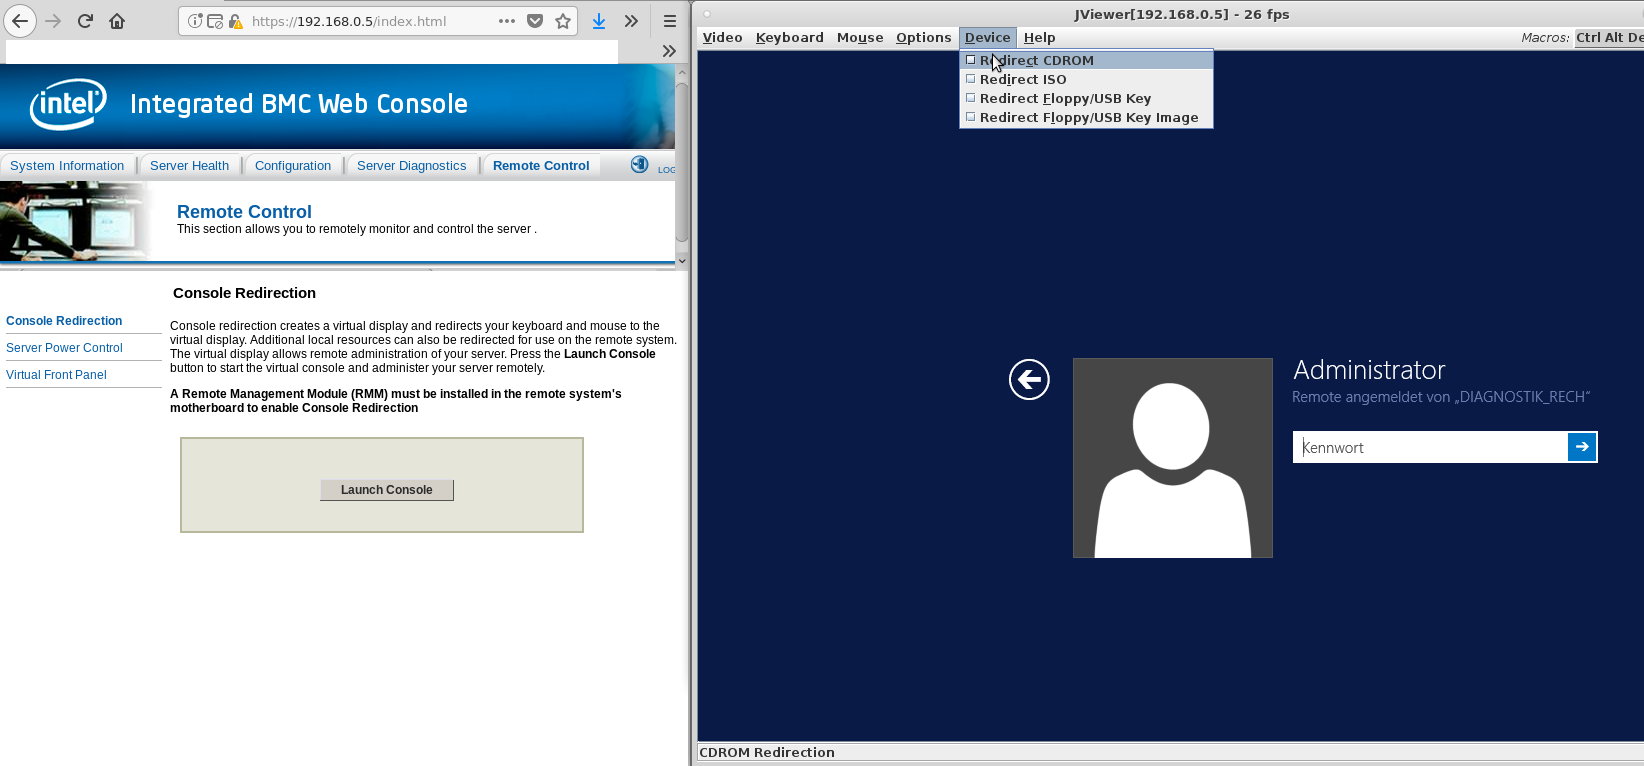
“The biggest network security threat today is a remote code execution exploit for Intel’s Management Engine.” “Every computer with an Intel chipset produced in the last decade would be vulnerable to this exploit, and RCE would give an attacker full […]
Open Source is about enabling users “Amazon, Microsoft, Google” and the White House, want to help make Open Source more secure… https://www.golem.de/news/openssf-150-millionen-us-dollar-sollen-open-source-absichern-2205-165382.html https://www.golem.de/news/openssf-linux-foundation-will-security-praxis-vereinheitlichen-2008-150036.html src of src: “White House OSS Mobilization Plan” 2022: https://openssf.org/blog/2022/05/11/testimony-to-the-us-house-committee-on-science-and-technology/ 2020: “The OpenSSF is a cross-industry collaboration […]
cyber is on heightened alarm levels … ya’ll know why. timeline of a successful attack on the most basic tools like: exiftool cve-2021-22204 (failed to properly validate parsed input) This was reported by a security researcher on April 7, 2021, […]